Cyber threats are becoming more frequent, sophisticated, and difficult to detect. Organizations now face a constant stream of suspicious activity, malware, phishing campaigns, compromised credentials, and emerging vulnerabilities. Traditional security tools can identify many known threats, but security teams often struggle to keep up with the sheer volume of information.
This is where artificial intelligence (AI) can make a significant difference. An AI-driven cyber threat intelligence platform can collect information from multiple sources, analyze large amounts of security data, identify patterns, and help security teams understand potential threats faster.
Instead of relying entirely on security professionals to manually review every alert, automated threat intelligence can help prioritize the information that requires attention.
Cyber threat intelligence is the process of collecting, analyzing, and interpreting information about potential or existing cyber threats.
Threat intelligence can include information about:

The goal isn't simply to collect data. Organizations need to turn that information into actionable intelligence that can improve their security decisions.
For example, knowing that an IP address has been associated with malicious activity is useful. Understanding whether that IP address is communicating with systems inside your organization—and what that activity means—is far more valuable.
Traditional threat intelligence processes can require analysts to gather information from numerous sources and manually determine whether individual indicators represent genuine threats.
AI can automate parts of this process.
An AI-driven platform can continuously process large datasets, identify relationships between seemingly unrelated events, and recognize patterns that may indicate malicious behavior.
Machine learning models can also help security systems identify unusual activity by comparing current behavior with historical patterns.
This doesn't mean AI replaces cybersecurity professionals. Instead, it can act as a force multiplier, helping analysts spend less time sorting through routine information and more time investigating serious threats.
One of the biggest advantages of an automated threat intelligence platform is its ability to collect information continuously.
Threat data may come from sources such as:
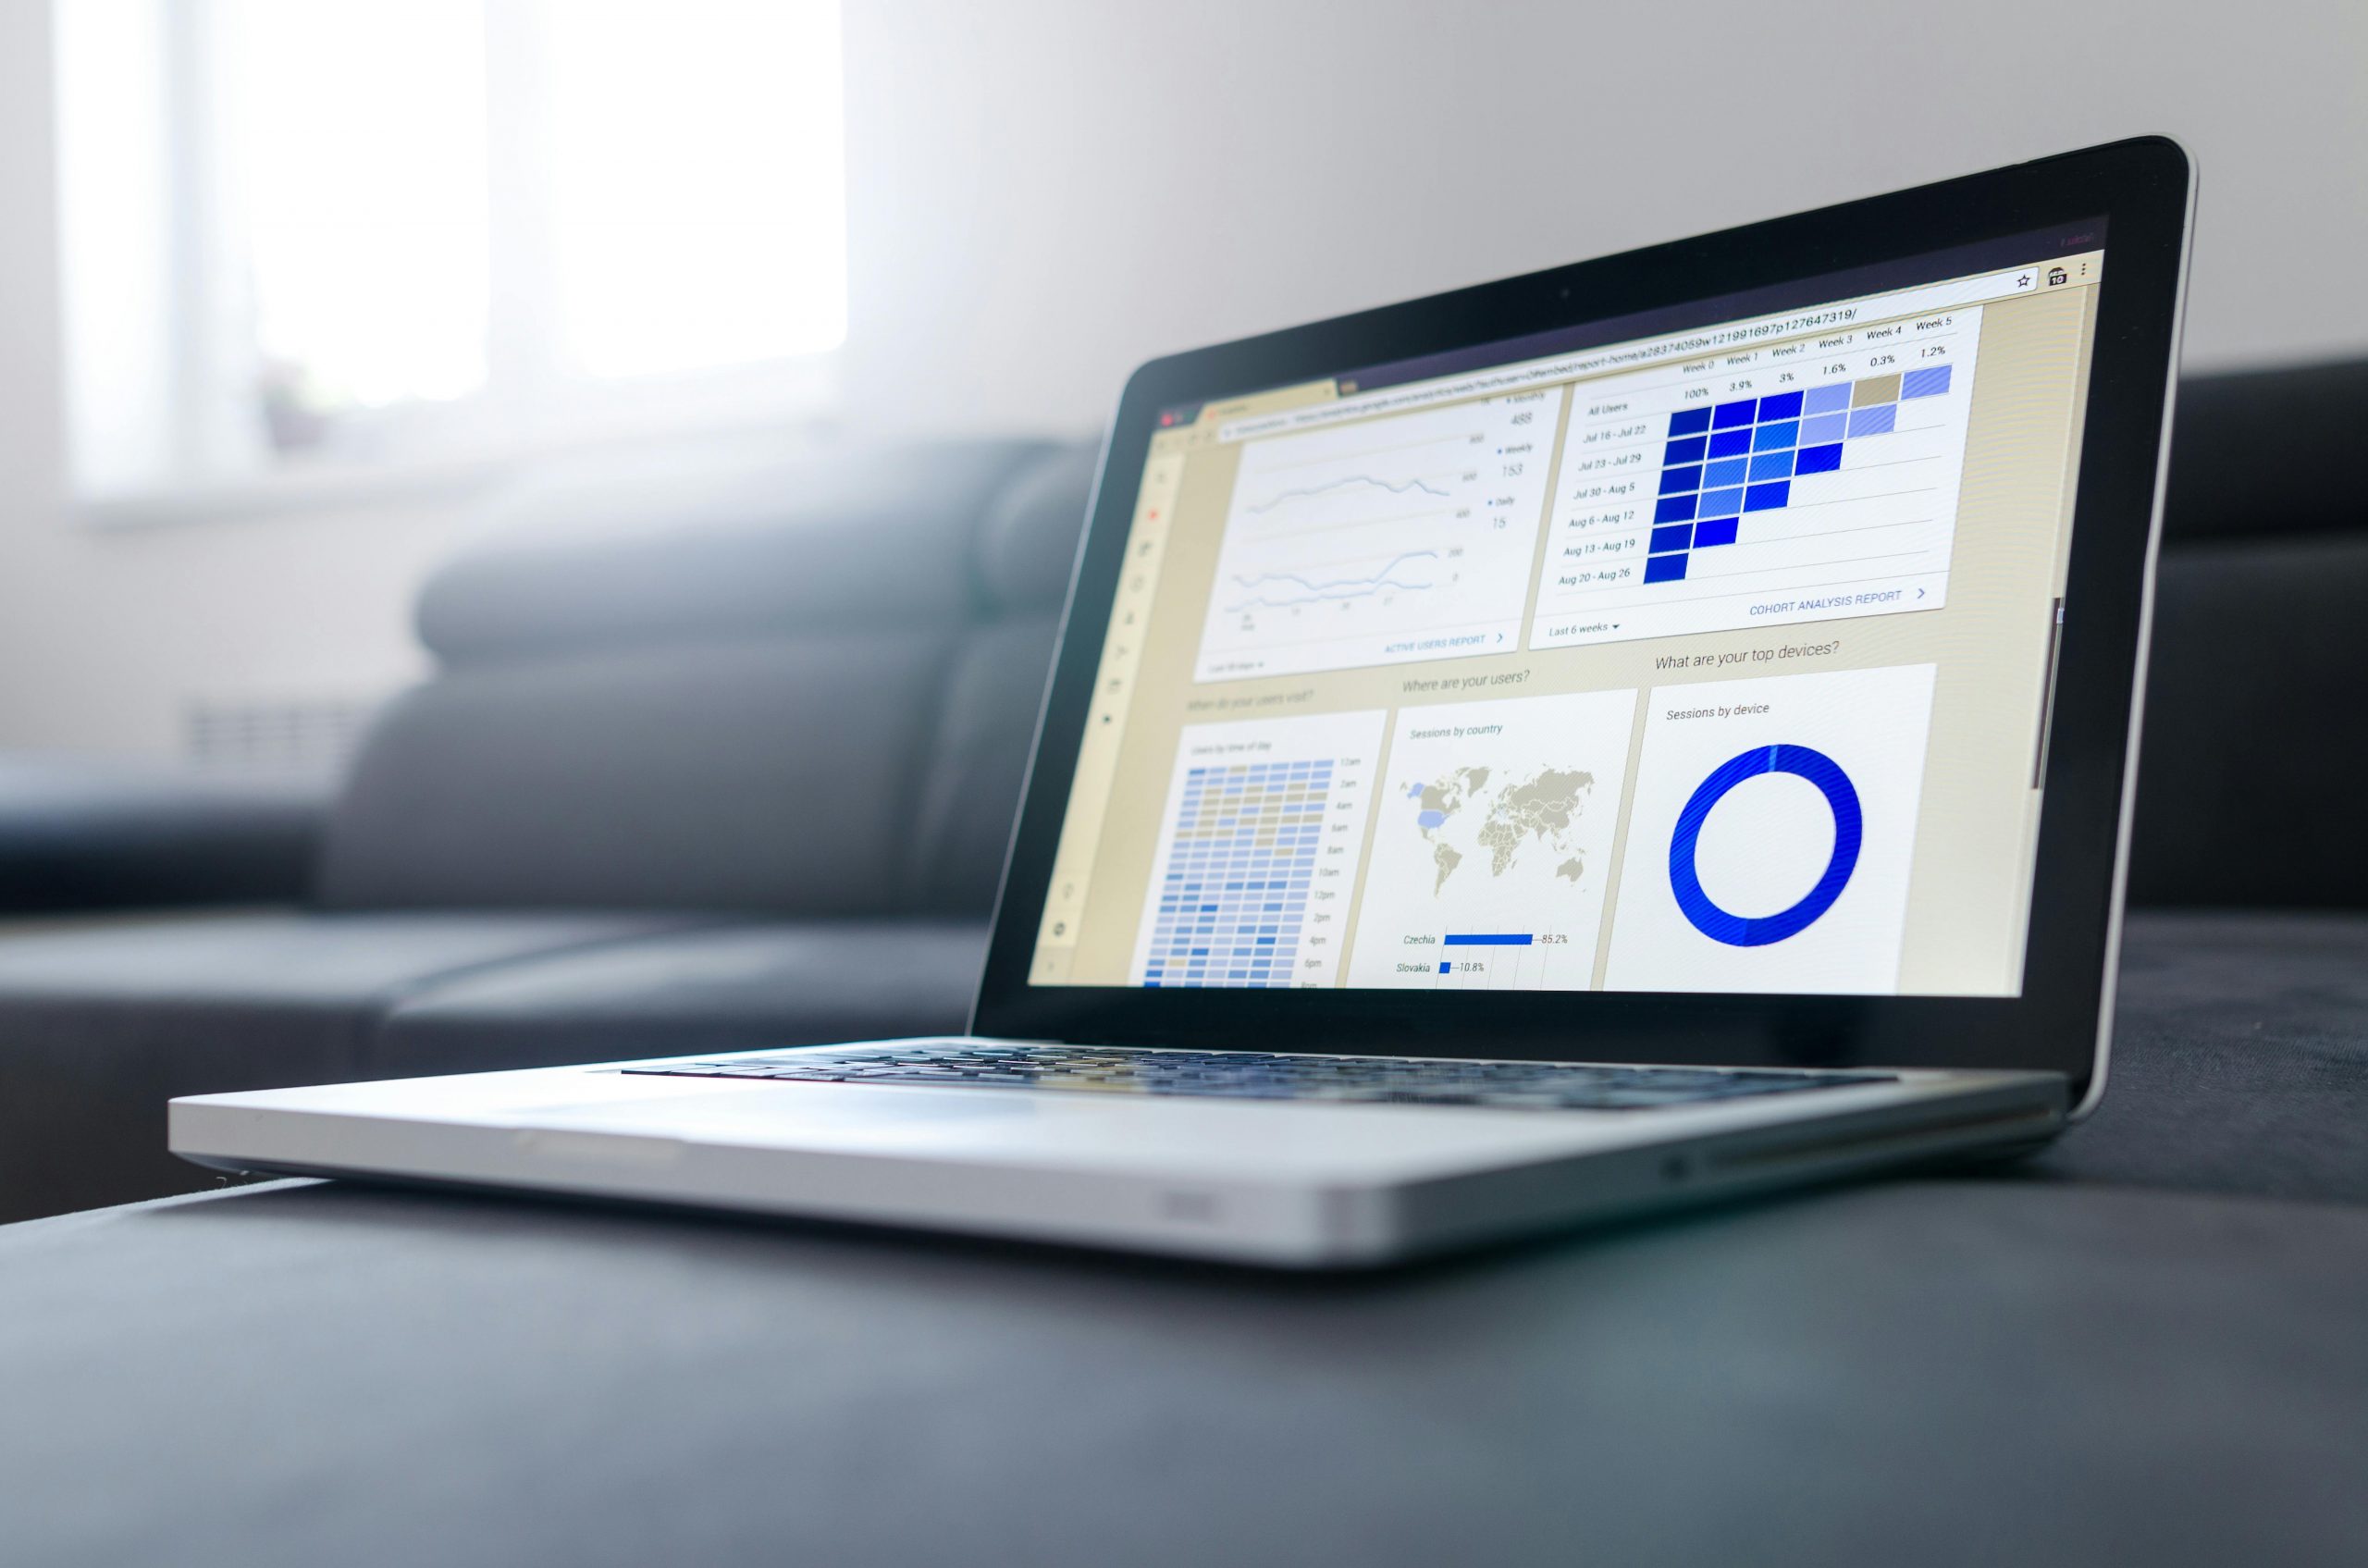
Automatically gathering this information creates a more complete picture of the organization's security environment.
Without automation, analysts may have to manually move information between multiple tools, increasing the possibility of delays and human error.
Modern organizations generate enormous quantities of security data every day.
A single suspicious event may not appear particularly dangerous when viewed independently. However, several related events may reveal a much larger attack pattern.
AI can analyze relationships between events and identify patterns across large datasets.
For example, a platform might detect a combination of unusual login activity, communication with a suspicious domain, and unexpected changes to an endpoint.
Individually, these events might generate separate alerts. Together, they could indicate that an account or device has been compromised.
Security teams frequently deal with alert fatigue.
When analysts receive hundreds or thousands of alerts, determining which events deserve immediate attention can become difficult. Important warnings can potentially get buried among low-priority notifications.
AI-driven threat intelligence can help prioritize alerts based on factors such as severity, context, historical behavior, and relationships with known threats.
Instead of presenting every event with the same level of importance, intelligent systems can help security teams focus on the alerts most likely to represent genuine threats.
Cybersecurity teams cannot rely solely on known threats.
Attackers constantly change malware, infrastructure, phishing techniques, and attack methods. A security platform that only searches for previously identified indicators may miss new variations.
AI can help identify anomalies and behavioral patterns that don't exactly match known threats.
This behavioral approach can be particularly valuable when attackers modify their tools to avoid traditional signature-based detection.

An AI-driven threat intelligence platform can also help organizations understand which vulnerabilities deserve immediate attention.
Not every vulnerability presents the same level of risk.
AI can help correlate vulnerability information with factors such as:
This can help organizations prioritize remediation based on actual risk rather than simply addressing vulnerabilities in numerical order.
When a security incident occurs, speed matters.
Threat intelligence can provide incident response teams with additional context about what they are seeing.
For example, analysts may be able to determine:
Automated intelligence can accelerate the investigation process by gathering relevant information before an analyst begins a deeper investigation.
An AI-driven threat intelligence platform becomes more useful when it can work with an organization's existing security infrastructure.
Potential integrations may include:
Integration allows threat intelligence to move beyond a standalone dashboard and become part of the organization's broader security workflow.
AI can process information quickly, but it isn't infallible.
Models can produce false positives, misunderstand context, or make incorrect assumptions based on incomplete information.
For this reason, cybersecurity professionals should remain involved in important decisions.
The best approach is generally AI-assisted security rather than blindly automated security.
AI can identify patterns, prioritize information, and recommend actions, while experienced analysts provide the context and judgment needed for high-impact decisions.
Organizations should also consider the security of the AI systems themselves.
Threat intelligence platforms may process sensitive information, including network data, security events, employee activity, and potentially confidential business information.
Organizations should establish appropriate controls around:
An AI security platform should strengthen an organization's defenses without creating a new security weakness.
AI provides significant benefits, but it isn't a magic solution.
Organizations may encounter challenges involving data quality, false positives, integration complexity, cost, model accuracy, and privacy.
Poor-quality threat data can also lead to poor-quality results. An AI system is only as useful as the information and context it receives.
Organizations should therefore evaluate platforms based on how well they integrate with existing infrastructure, how transparent their analysis is, and how effectively security teams can validate and act on recommendations.
Cybersecurity is becoming increasingly data-driven.
As organizations generate more security information and attackers continue developing new techniques, automation will become increasingly important.
Future threat intelligence platforms are likely to combine AI, machine learning, behavioral analytics, automation, and human expertise to provide faster and more contextual security analysis.
The objective isn't simply to generate more alerts. It is to help organizations understand threats earlier and respond more effectively.
An AI-driven cyber threat intelligence platform can transform how organizations collect, analyze, and respond to security information.
By automating data collection, identifying patterns, prioritizing alerts, correlating threats, and providing additional context, AI can help security teams manage an increasingly complex threat landscape.
However, successful cybersecurity still requires more than technology. Strong security practices, skilled professionals, effective policies, reliable data, and human judgment remain essential.
AI should not replace cybersecurity expertise. It should help security teams use that expertise more effectively.
 Like
1
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0